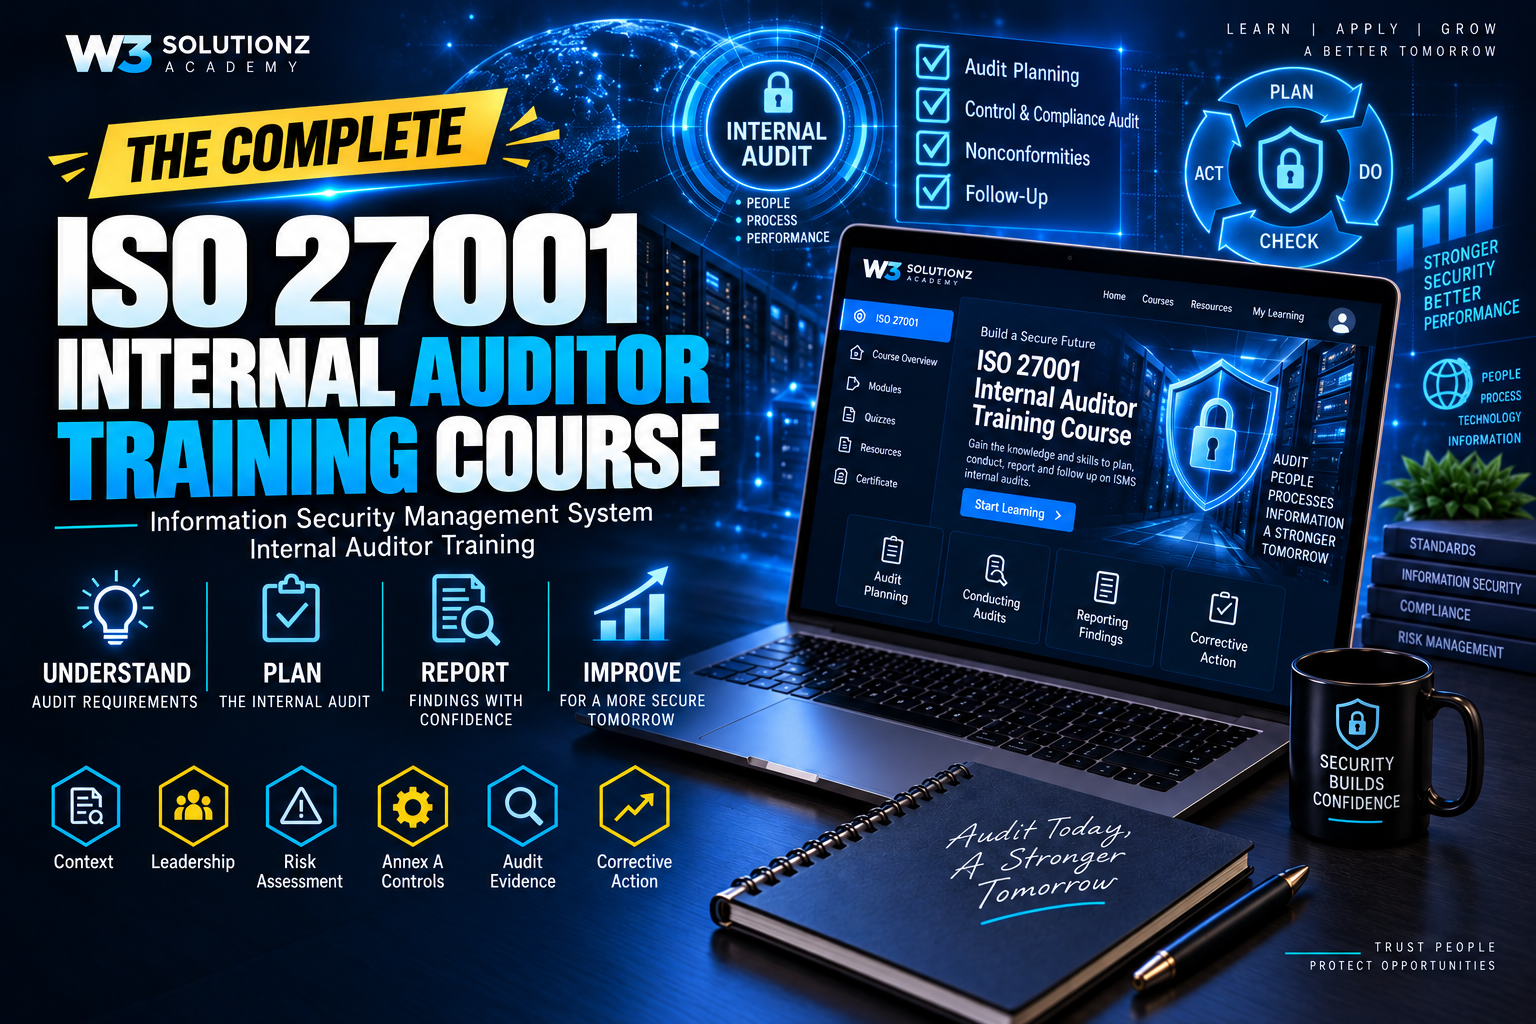
About Course
Develop ISMS internal audit skills through 12 modules and 36 text lessons with exercises and model feedback. Evaluate risk assessment, treatment, the Statement of Applicability, all four Annex A control groups and security performance. Includes selected control examples, not specialist implementation training for all 93 controls. Practise audit planning, sampling, interviews, findings, reporting and corrective-action follow-up. Includes a 40-question exam and a marked practical assignment. Total workload: 14 hours excluding breaks.
Course Content
ISMS foundations and audit criteria
-
Course route and the internal auditor role
-
Information security and the management system
-
ISO/IEC 27001, Annex A and related guidance
Context, leadership and planning
Risk assessment, treatment and applicability
Support and ISMS operation
Organizational and people controls
Physical and technological controls
Evaluation and improvement
Audit principles and programme management
Audit preparation, planning and sampling
Conducting the information-security audit
Findings, reporting and follow-up
Integrated practice and workplace application
Assessment
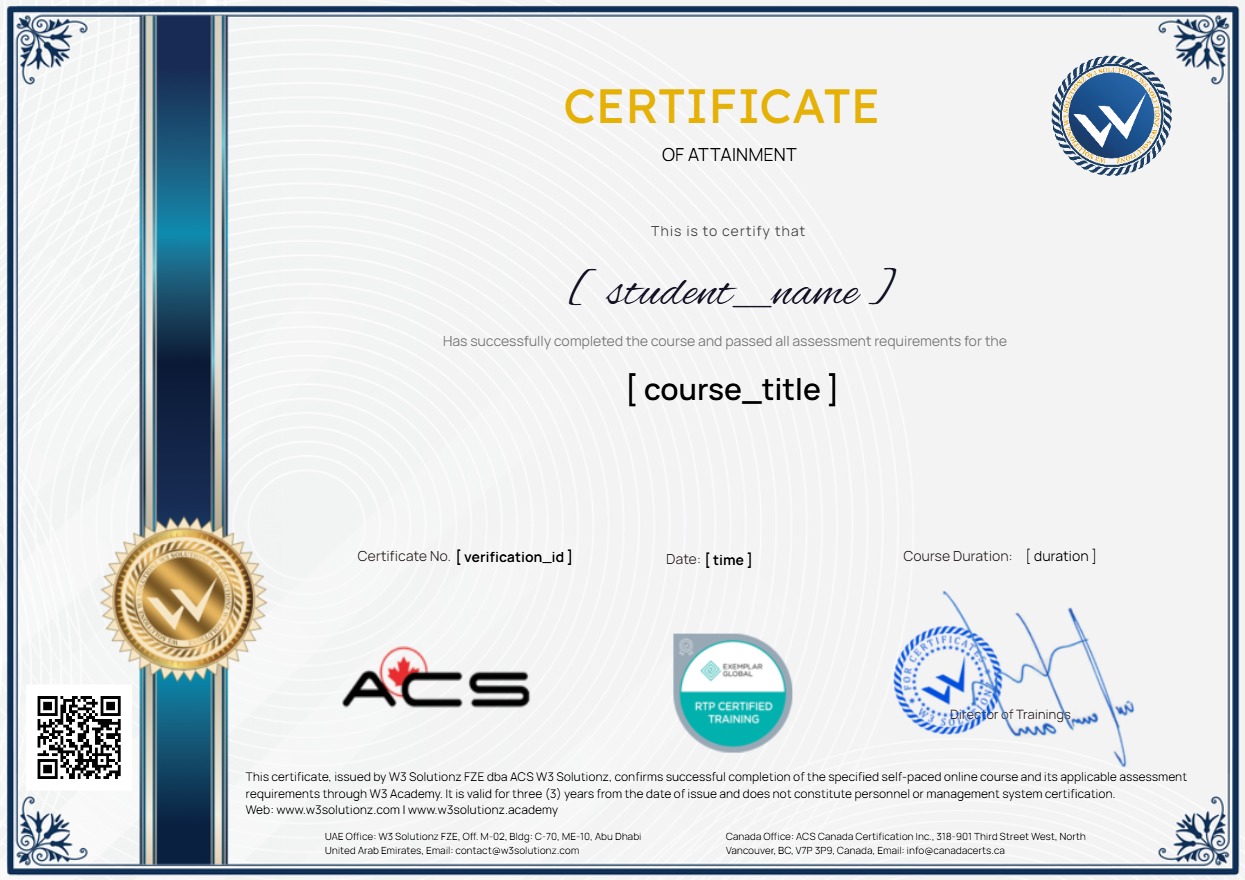
Earn a certificate
Add this certificate to your resume to demonstrate your skills & increase your chances of getting noticed.
Student Ratings & Reviews

No Review Yet