Skip to content
W3 SolutionzACADEMY

ISO/IEC 27017:2026 Cloud Security Controls Lead Auditor Training

Wishlist Share

Share this course

Help a colleague take their next step.

About Course

40 hours: 36 standard and audit foundation lessons, 16 advanced lead-audit lessons, four practical assignments including observed individual audit leadership, and a 40-question final exam. AED 999. W3 completion only. This training does not itself grant professional registration, accreditation or authority to certify organizations. This is lead-auditor training for adopted cloud controls and commitments; the subject standard is guidance, not a standalone management-system requirements standard. Do not invent control identifiers; verify them in an authorized current edition.

What Will You Learn?

  • LO01: Interpret the subject standard and applicable audit criteria
  • LO02: Evaluate domain-specific evidence and performance
  • LO03: Manage a risk-based programme and feasible plan
  • LO04: Lead an independent competent audit team
  • LO05: Interview sample and corroborate evidence
  • LO06: Write and classify defensible findings
  • LO07: Report bounded conclusions and evaluate corrective action
  • LO08: Demonstrate observed leadership and verify effectiveness

Course Content

Cloud audit foundations and edition control
Explain cloud models, the role of ISO/IEC 27017 and a defensible hierarchy of audit criteria.

  • Course route and lead auditor responsibilities
  • What ISO/IEC 27017 contributes
  • Edition control and selecting audit criteria

Scope, risk and shared responsibilities
Map cloud boundaries, risks and customer/provider responsibilities to verifiable controls.

Information lifecycle and service exit
Evaluate cloud asset inventories, data protection, retention and verified service exit.

Identity, isolation and secure configuration
Audit identity, tenant separation and configuration controls using authorized evidence.

Administration, monitoring and networks
Evaluate privileged operations, useful monitoring and connected network safeguards.

Suppliers, incidents and resilience
Assess provider assurance, incident coordination and recovery dependencies.

Control evaluation and improvement
Evaluate meaningful indicators, governance decisions and corrective-action effectiveness.

Auditor competence and audit programme
Apply audit principles, competence and risk-based programme management.

Audit preparation and sampling
Prepare objectives, criteria, a feasible plan and risk-informed samples.

Conducting a cloud internal audit
Conduct interviews and assess cloud evidence while protecting confidentiality.

Findings, reporting and follow-up
Write supported findings, communicate limitations and verify corrective actions.

Integrated practice and assessment preparation
Integrate cloud-control audit skills and recognize the limits of course completion.

Lead audit preparation and programme
Advanced leadership and practical application to shared responsibility, privileged identities, supplier evidence and service exit.

Audit execution and team leadership
Advanced leadership and practical application to shared responsibility, privileged identities, supplier evidence and service exit.

Findings communication and reporting
Advanced leadership and practical application to shared responsibility, privileged identities, supplier evidence and service exit.

Corrective action follow up and assessment
Advanced leadership and practical application to shared responsibility, privileged identities, supplier evidence and service exit.

Earn a certificate

Add this certificate to your resume to demonstrate your skills & increase your chances of getting noticed.
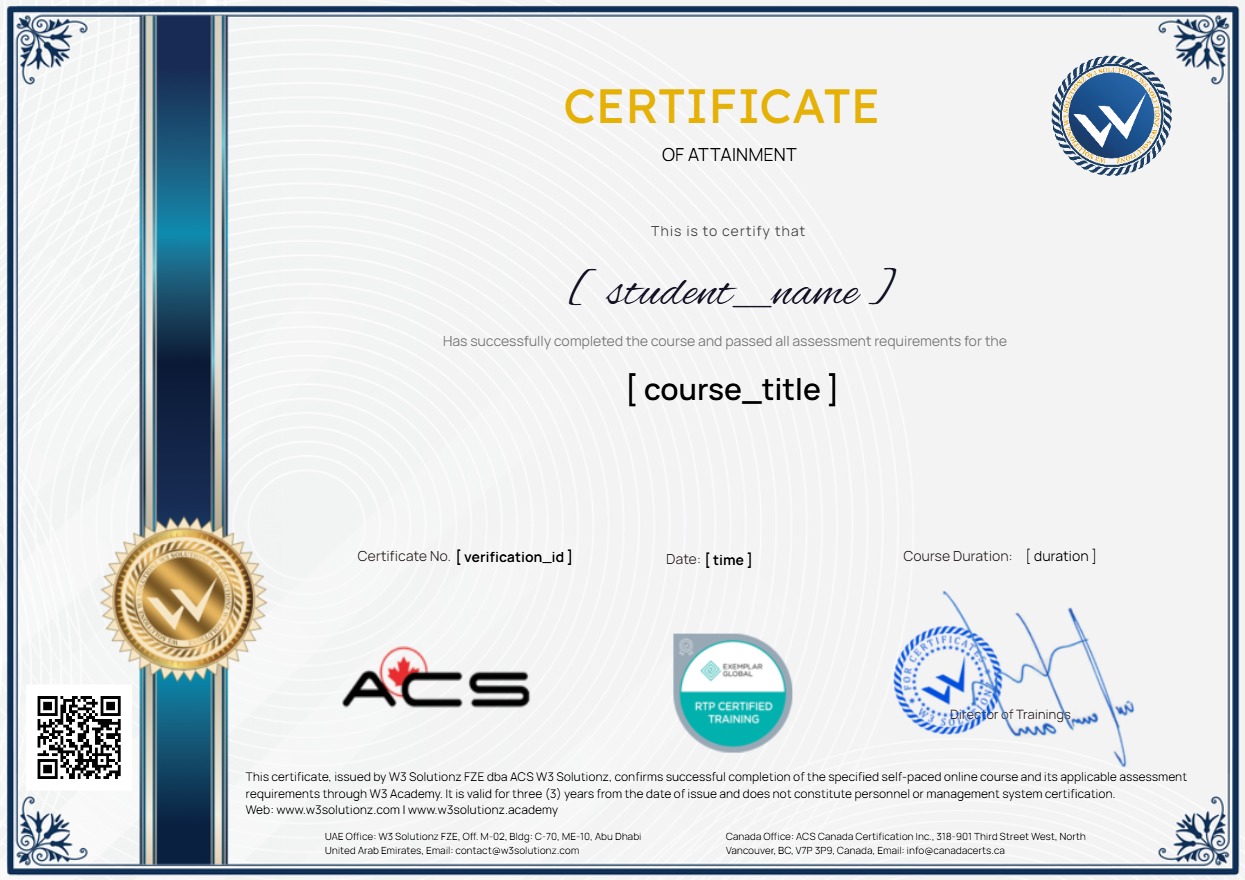
selected template

Student Ratings & Reviews

No Review Yet
No Review Yet

Want to receive push notifications for all major on-site activities?

✕