Skip to content
W3 SolutionzACADEMY

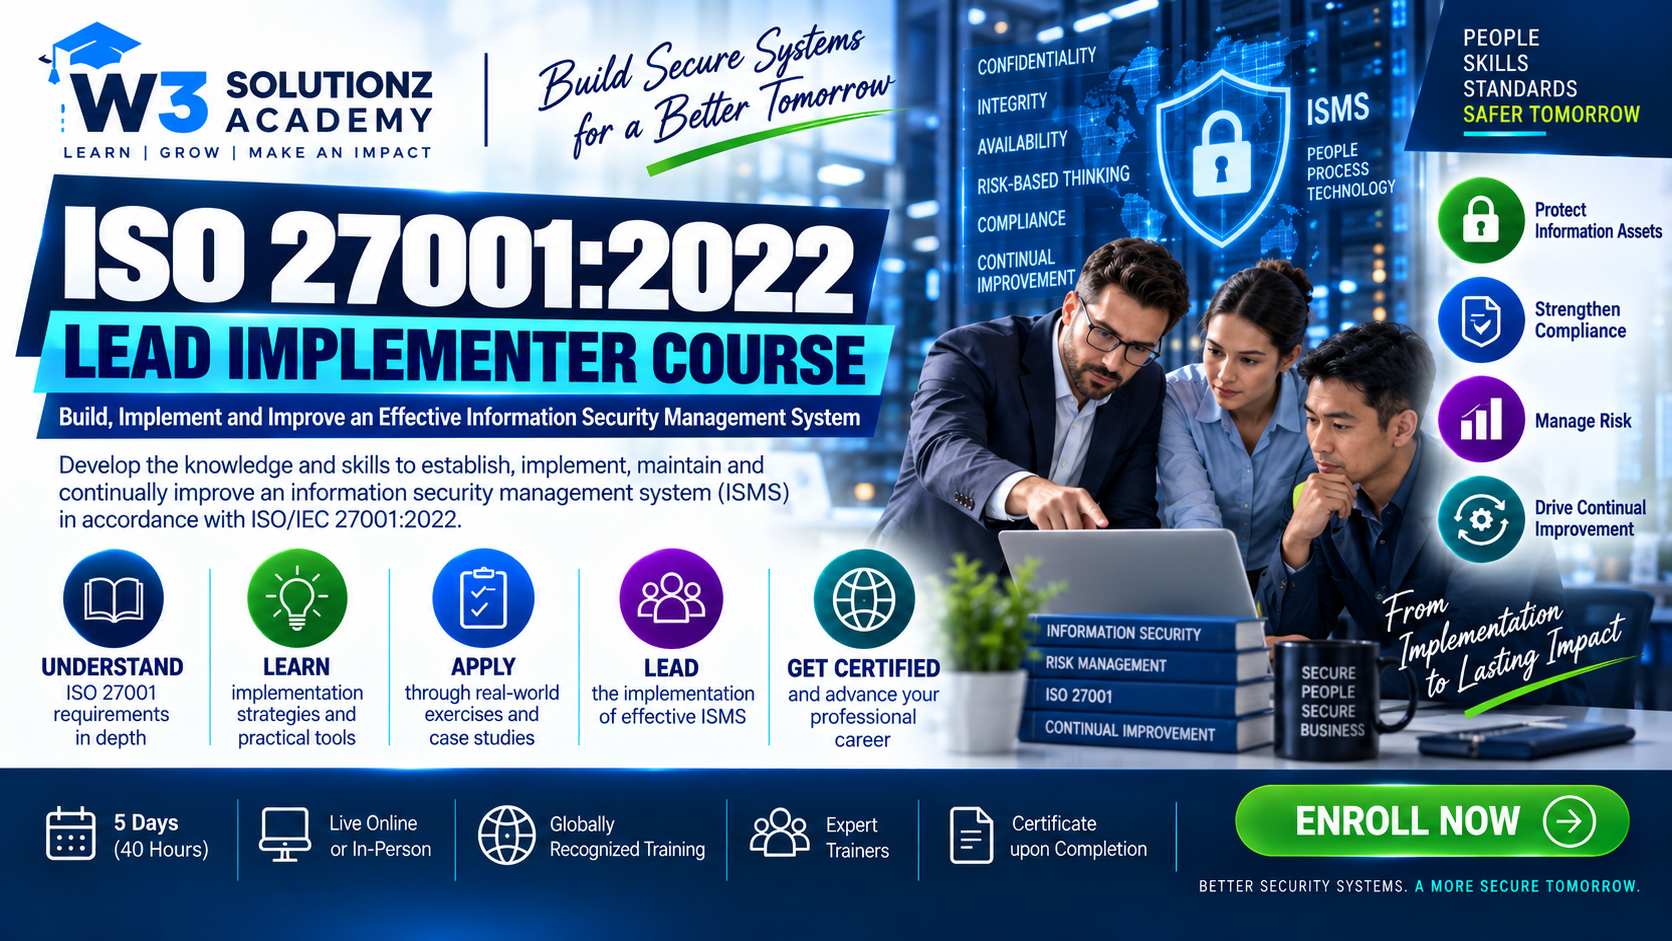
ISO/IEC 27001:2022 Lead Implementer Training

Categories: Information Security
Wishlist Share

Share this course

Help a colleague take their next step.

About Course

Complete 40-hour ISMS implementation course with 40 text lessons,93 Annex A control implementation notes, risk/SoA/treatment templates, seven marked practical quizzes, five knowledge checks,40-question final exam and four typed assignments including an observed workshop and controlled capstone. Covers Clauses 4–10 and the 2024 climate amendment with a connected fictional SaaS case and private instructor marking guidance. AED 999 and 365-day access retained. W3 course completion only; Exemplar Global Recognized Training.

What Will You Learn?

  • LO01: Explain ISMS outcomes, determine context/scope and establish leadership and an implementation charter
  • LO02: Map information and dependencies and perform consistent CIA-based risk assessment/evaluation
  • LO03: Select treatment, prepare a defensible SoA, obtain owner decisions and plan objectives/changes
  • LO04: Provide resources, competence, communications, documented information and organizational/access governance
  • LO05: Implement supplier/cloud, obligation, people and physical security arrangements
  • LO06: Design, deploy and verify technological controls including secure development
  • LO07: Operate risk treatment, manage incidents/resilience and evaluate meaningful performance
  • LO08: Establish impartial audit and management review and lead evidence-based steering decisions
  • LO09: Control consequences, investigate causes/extent and verify corrective action and improvement
  • LO10: Lead resourced rollout, assess readiness honestly and hand over sustainable ownership

Course Content

ISMS foundations, context and project
Information-security outcomes, standard structure, boundaries, governance and baseline implementation.

  • Information-security outcomes and implementer responsibilities
  • The 2022 requirements, Annex A and supporting guidance
  • Context, interested parties, climate and scope
  • Leadership, policy, roles and project baseline
  • Context, scope and implementation charter

Information assets and risk assessment
Information flows, risk criteria, identification, analysis and evidence-based prioritization.

Treatment, Statement of Applicability and planning
Necessary controls, Annex A comparison, treatment plans, approvals, objectives and changes.

Support and organizational control design
Resources, competence, awareness, communication, information governance and access ownership.

Supplier, people and physical implementation
External/cloud assurance, obligations, people lifecycle and physical protection.

Technological control implementation
Endpoint, data, infrastructure, monitoring, cryptographic and secure-development controls.

Operational risk, incidents and resilience
Operating evidence, reassessment, incident management, continuity and measurement.

Audit, management review and leadership
Impartial assurance, evidence-based review and observed steering decisions.

Corrective action and continual improvement
Consequence control, cause/extent investigation, effectiveness and improvement.

Rollout, readiness and sustainable handover
Resourced integration, honest readiness, certification boundaries and final assessment.

Earn a certificate

Add this certificate to your resume to demonstrate your skills & increase your chances of getting noticed.
selected template

Student Ratings & Reviews

No Review Yet
No Review Yet